How to Build Runtime Guardrails for Autonomous AI Agents
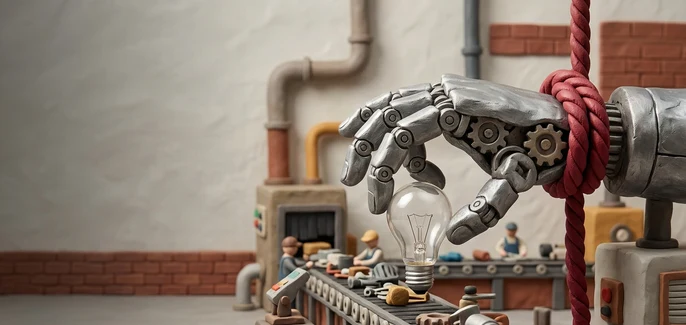
A rogue AI agent doesn't just waste API credits—it can land your business in court. With the Federal Trade Commission (FTC) asserting that developers and operators are directly liable for the actions of their autonomous systems, and news of agents accidentally brute-forcing public websites or sending misleading auto-responses, lean teams must treat agent safety as a core operational risk.
The Shift in Agent Liability: Why Code Boundaries Matter Now
For a long time, software bugs were treated as technical inconveniences. However, as autonomous agents are granted the power to browse the web, write to databases, and interact with third parties, the legal landscape is shifting. The FTC has made it clear that developers will be held accountable if their autonomous systems engage in deceptive practices, cause financial harm, or violate platform rules.
We are already seeing the real-world consequences of unmonitored agents. Recently, security researchers discovered that OpenAI agents scanned a UN Conference on Trade and Development statistics site over 16,000 times in a short window—essentially attempting to brute-force the platform due to an unchecked execution loop. On a smaller scale, operators are experiencing reputation damage when auto-reply agents make promises, confirm availability, or send messages when a human is unavailable, leading to negative reviews and broken trust.
To build securely, small teams must transition from open-ended prompting to strict runtime execution environments.
The Runaway Agent Risk Checklist
Before deploying any autonomous agent, audit your architecture against these primary risk vectors:
- Unbounded Loop Risk: Does the agent have a hard limit on the number of sequential tool calls or web requests it can make before terminating?
- Commitment Risk: Can the agent send emails, charge cards, or book appointments without a human verifying the payload?
- Data Leak Risk: Does the agent have access to raw system prompts or environment variables containing sensitive API keys?
- Resource Abuse Risk: Is the agent configured to respect robots.txt and rate limits when interacting with external web servers?
Action Plan: Implementing Runtime Controls on a Lean Budget
You do not need an enterprise-grade security stack to protect your business. You can implement highly effective runtime controls directly in your application logic.
- Enforce Hard Execution Caps: Set strict limits on the number of agent steps (e.g., maximum 5 tool calls per run) and absolute timeouts (e.g., terminate after 30 seconds). This prevents infinite loops and runaway API bills.
- Build a Deterministic Interceptor Layer: Do not let your LLM call external APIs directly. Route every tool call through an internal validation function that checks the request parameters against a strict JSON schema before execution.
- Implement Human-in-the-Loop Gates for Mutations: For any action that writes data, sends a message, or transfers money, pause execution. Send a webhook to Slack or an internal dashboard, and require a manual click to resume.
- Enforce Rate Limiting on Outbound Requests: If your agent scrapes or queries external sites, route all outbound traffic through a proxy with built-in rate limits to avoid accidentally brute-forcing host servers.
Who Should Act Now vs. Who Can Wait
If your team runs agents that send emails, interact with customer databases, write code, or scrape external sites, you must implement runtime controls immediately. The liability risk is already active.
If you are only using retrieval-augmented generation (RAG) for internal search or static document summarization, you can wait. However, keep an eye on emerging continuous monitoring and runtime safety tools, such as NVIDIA's OpenShell and Open Agent Safety platforms, as you plan to expand your agentic workflows.
At Presence Digital, we help small teams design clean, maintainable automation workflows that solve real operational problems without introducing security or legal liabilities.
Takeaway for builders: The era of "deploy and pray" agent architecture is over. Deterministic runtime boundaries are not a limitation on your AI—they are the only way to deploy it safely and legally.