How to Set Up Application Tests Without Over-Engineering
Why do test suites get over-engineered, and why is it so hard to get the architecture right? Sometimes the codebase offers no good seams: business rules are tangled into UI components and controllers, so testing anything useful means dragging in half the application. Sometimes the strategy is the problem: every acceptance criterion becomes its own end-to-end test, coverage becomes a target in itself, or AI generates piles of shallow unit tests that look reassuring but prove little.
These problems often reinforce each other. When rules are hard to isolate, teams reach for browser tests. When those tests make CI slow, they add more unit tests without deciding what behavior matters. The result is a large suite that is costly to maintain and still misses important failures.
A better goal is not “more tests.” It is fast, trustworthy feedback at the right level. That means testing business rules close to where they live, checking a few important journeys through the real interface, and using the cheapest tools available for mistakes that tests do not need to catch.
Choose tests by the question they answer
A useful test strategy starts by separating two different questions. First: does this business rule behave correctly? Second: can a user complete an important task through the application? Those questions deserve different tests.
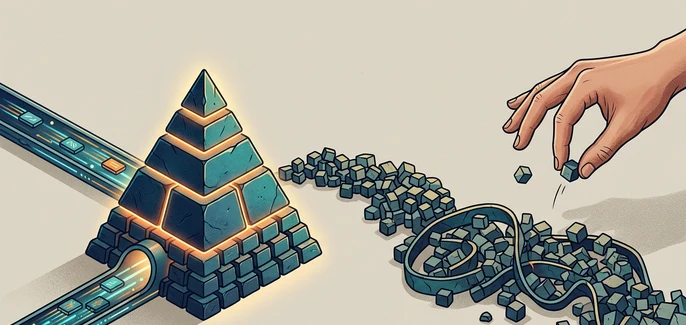
Consider a team with a React app of more than 300 features. For two years, they wrote one Cypress acceptance test for every acceptance criterion. CI eventually grew past 30 minutes. Their change was not to abandon end-to-end tests. They began separating business rules from happy-path user journeys: test the rules with fast, low-level unit tests, then retain a small number of acceptance tests for the important journeys. The result is a testing pyramid: many fast checks at the base, fewer boundary and integration checks in the middle, and a small set of end-to-end checks at the top.
That approach is a useful example, not a rule that every team must copy. A team building a UI-heavy product may prefer the testing trophy, which emphasizes integration tests that exercise components together. A service with complex domain rules may put more weight on unit tests. Neither metaphor is a quality standard. The practical question is whether a test gives reliable feedback about behavior at an appropriate cost.
Use an end-to-end test when the risk is that a critical user journey fails across several parts of the system: for example, a customer cannot submit an order. Use an integration test when the risk sits at a boundary, such as a handler mapping an API request to a database operation. Use a unit test when a business rule has meaningful inputs and outputs that can be checked without starting the application.
Do not compare teams by one blended coverage number. Coverage can tell you which code a particular test run executed; it cannot tell you whether tests assert the right outcomes, whether the most important paths are protected, or whether a fragile test will block releases. Keep coverage available as a diagnostic, ideally scoped to relevant modules, but review test quality and feedback time alongside it.
Shared and common code deserves deliberate attention. A formatting helper may need little ceremony, but a shared permission check, pricing rule, date calculation, or data transformation can affect many features at once. Give consequential shared behavior direct tests. Otherwise, a change can break several consumers and the failure may surface far from the code that caused it.
Set up the layers in a maintainable order
Do not start by buying a new test tool or writing hundreds of cases. First make it cheap to identify the kind of failure you care about. Then add layers in sequence, so each new class of test covers a gap rather than duplicating work.
Establish static checks first. Run TypeScript or your language’s type checker, linting, and formatting checks locally and in CI. These are usually the cheapest way to catch invalid types, inconsistent style, and common mistakes. Make the commands easy to run and keep their output clear. Static checks do not prove that business behavior is correct, but they should catch basic problems before a slower test suite starts.
Create seams around business rules. Identify a rule currently buried in a component, controller, or request handler. Extract it into a small domain module or pure function that accepts explicit inputs and returns a result. For example, a component that decides whether a user can edit a record can call a permission function with the user and record, instead of mixing that decision into rendering logic. Avoid building a generic framework for hypothetical future rules. Extract only enough to make real behavior understandable and testable.
Test the rules directly. Add focused unit tests for important outcomes and meaningful edge cases. For a permission rule, test an allowed user, a disallowed user, and the boundary conditions that could change the decision. Assert observable results, not private implementation details such as which helper was called. Keep tests independent and quick. If a rule is trivial and has no meaningful risk, it may not need its own test.
Add integration tests at real boundaries. Test a thin layer where application code meets something external or shared: an API, database, queue, or framework adapter. Verify the mapping that matters, such as whether a request is validated and the correct record is saved. Use a representative test database or a controlled dependency where appropriate. Do not make every unit test talk to a live service; boundary tests are more valuable when their setup and failure modes are intentional.
Keep a handful of end-to-end journeys. Choose the paths whose failure would seriously disrupt users or operations, such as signing in, creating a core record, or completing a key workflow. Exercise those journeys through the real application. Avoid turning every acceptance criterion into a separate browser test. Lower-level tests can cover the variations in business rules; end-to-end tests should confirm that the main pieces still work together.
Shape CI around fast feedback. Run formatting, linting, type checks, and fast unit tests first. Put integration and browser suites after them, and run independent work in parallel when your CI environment supports it. Split a slow suite by stable test groups or files rather than making every job run everything. Set a time budget for the pipeline and investigate when it is exceeded; a budget is a trigger for review, not a promise that tests should be removed indiscriminately. Keep failure output actionable so developers can tell which layer failed.
Review AI-generated tests like production code. Ask what distinct behavior each test protects, whether the assertion would fail for a real regression, and whether a simpler test at a lower layer would answer the same question. Delete tests that only mirror implementation, repeat existing assertions, or pass without checking a meaningful outcome. AI can help draft cases, but it cannot decide which risk deserves the maintenance cost.
This sequence is deliberately modest. If your team has no tests, it is safer to add one useful rule test and one critical journey than to attempt a sweeping test-architecture rewrite. Keep the application working at every step, and let recurring changes reveal where the next seam or test is worth creating.
Make the suite useful in daily work
A test suite is part of the development workflow, not a separate quality project. Developers need to know what to run before pushing, what CI runs on every change, and what can run on a slower schedule. Write down those commands and keep them aligned with CI. If a test is flaky, identify and fix the source of instability rather than teaching the team to rerun it until it passes.
Review failures by layer. A type error should not require reading browser-test logs. A unit test failure should point to the rule and expected outcome. An end-to-end failure should make clear which user journey failed and provide enough context to investigate. Clear boundaries reduce the temptation to add redundant tests as insurance.
Also agree on what not to test. Do not add a browser test solely because a requirement is written as an acceptance criterion. Do not add unit tests for every line to improve a headline coverage number. Do not mock every collaborator until a test no longer resembles real behavior. These shortcuts can make the suite larger while making its signal weaker.
Teams should act now if slow or flaky CI is regularly interrupting delivery, if important behavior has no clear test home, or if developers cannot tell which checks to trust. Teams with a small, stable application and no recurring testing pain can wait before adopting a new framework or reorganizing the whole codebase. Start with the next risky change and add the smallest useful check.
There are limits to this approach. Pure functions are not a substitute for testing actual infrastructure behavior, and a handful of end-to-end tests cannot cover every combination of user input and system state. The aim is not complete certainty. It is a maintainable spread of checks that catches different classes of failure without making every change wait on the slowest layer.
A short checklist before adding a test
What specific failure or behavior should this test detect?
Can a static check catch the problem more cheaply?
Does this belong in a unit, integration, or end-to-end test?
Is the behavior important enough to justify future maintenance?
Does an existing test already provide the same signal?
Will the test give a clear, reliable failure in CI?
Presence Digital, an AI engineering studio, helps teams set up fast, reliable test and CI pipelines. Whether you do it with outside help or in-house, begin with one practical next action: take a slow or confusing test in your current suite and decide whether it belongs at a lower layer, needs clearer assertions, or should be deleted.
Takeaway for operators and builders: a strong test suite is not the one with the most tests; it is the one that tells you quickly whether the behavior that matters still works.
Newsletter
New articles, in your inbox
One email when we publish. No digests and no product pitches. Unsubscribe any time. Privacy policy